Study in Pictures🌐 English (United States)
Cybersecurity Fundamentals Illustrated

Digital book in PDF · read it on your phone or print it

Cybersecurity Fundamentals Illustrated

The CIA triad, which key does what, the ports, network zones, MFA, access control, incident response and risk math. Every topic gets its own page: the drawing first, then what you need to remember.

  • 69 illustrated pages
  • English
  • 30-day guarantee
US$ 27US$ 63
Get the book · US$ 27

Price shown for: United States. In other countries, the checkout shows the price that applies there.

About this book

What it is

The CIA triad, which key does what, the ports, network zones, MFA, access control, incident response and risk math. Every topic gets its own page: the drawing first, then what you need to remember.

Who This Book Is For
  • You're starting Security+
  • Your exam date is close
  • You already work in IT
What it covers
  1. Security Basics
  2. Cryptography and PKI
  3. Threats, Attacks and Vulnerabilities
  4. Networks and Security Architecture
  5. Identity and Access
  6. Security Operations
  7. Governance, Risk and Compliance
  8. Exam-Day Review
Language
English (United States)
Pages
69
Format
Digital book in PDF · read it on your phone or print it
Price
US$ 27 (United States)
Delivery
This is a digital PDF book sent to your email: nothing is printed or shipped.
30-Day Guarantee
30-day guarantee: if a file doesn't open, if the content isn't what the product page describes, if you were charged twice or the email never arrived, write to us and we'll refund you in full.

Look Inside the Book

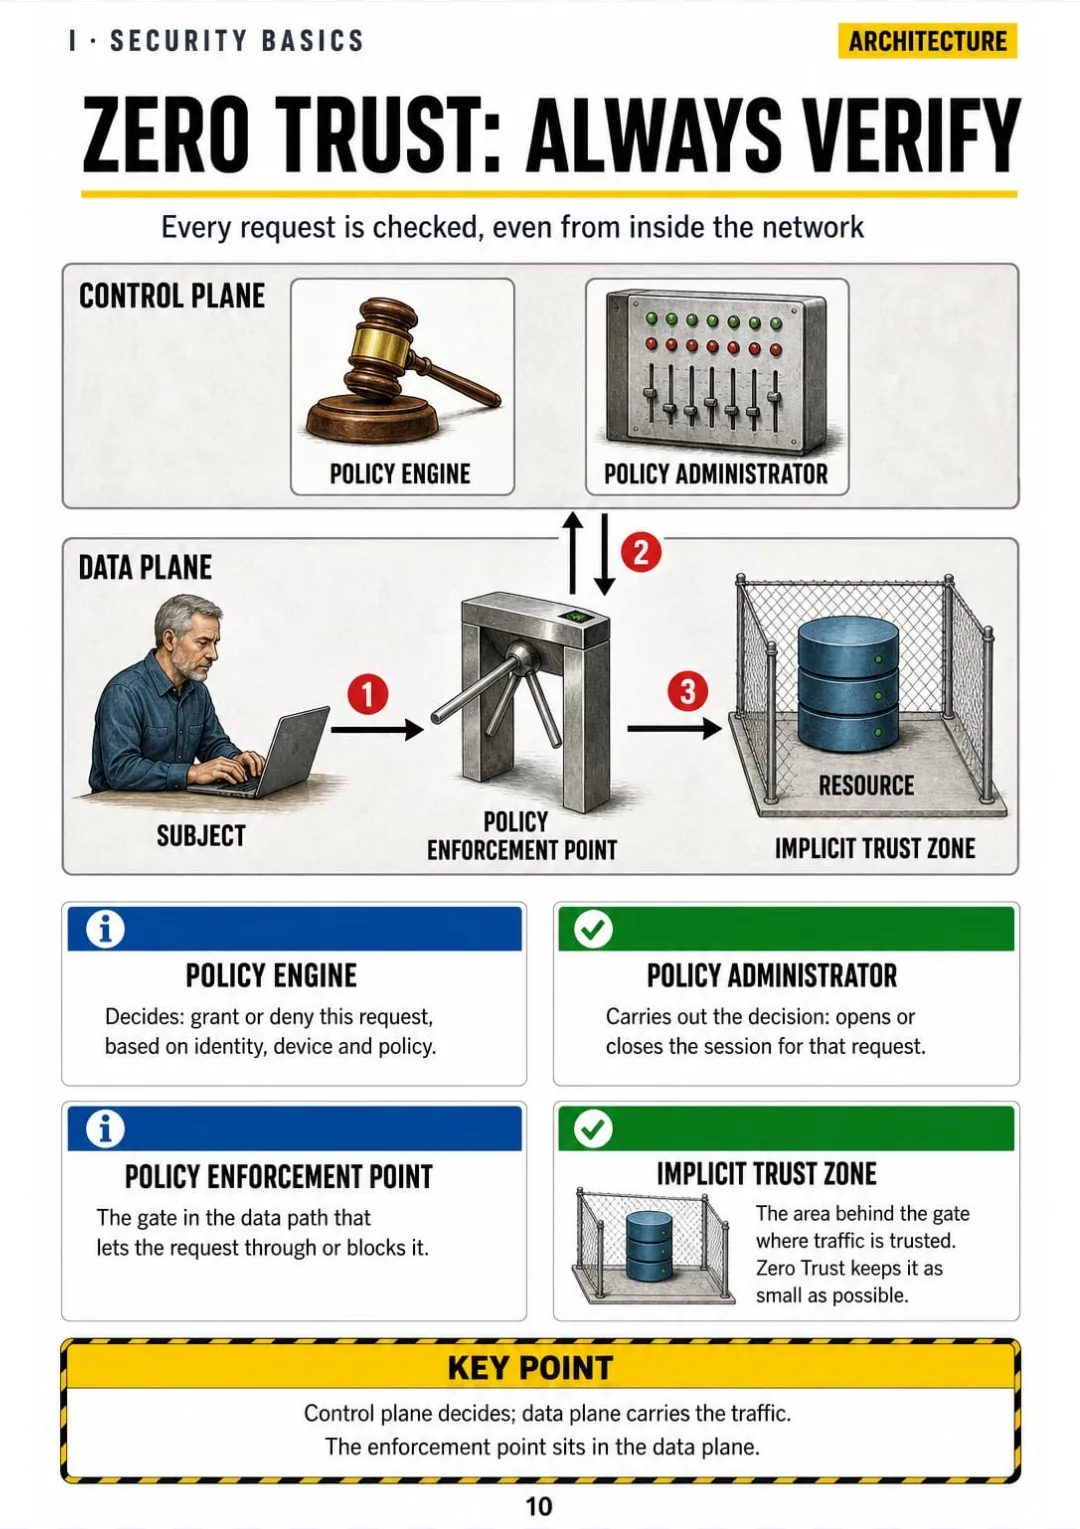
Policy Engine decides · Policy Administrator executes · Enforcement Point lets it through
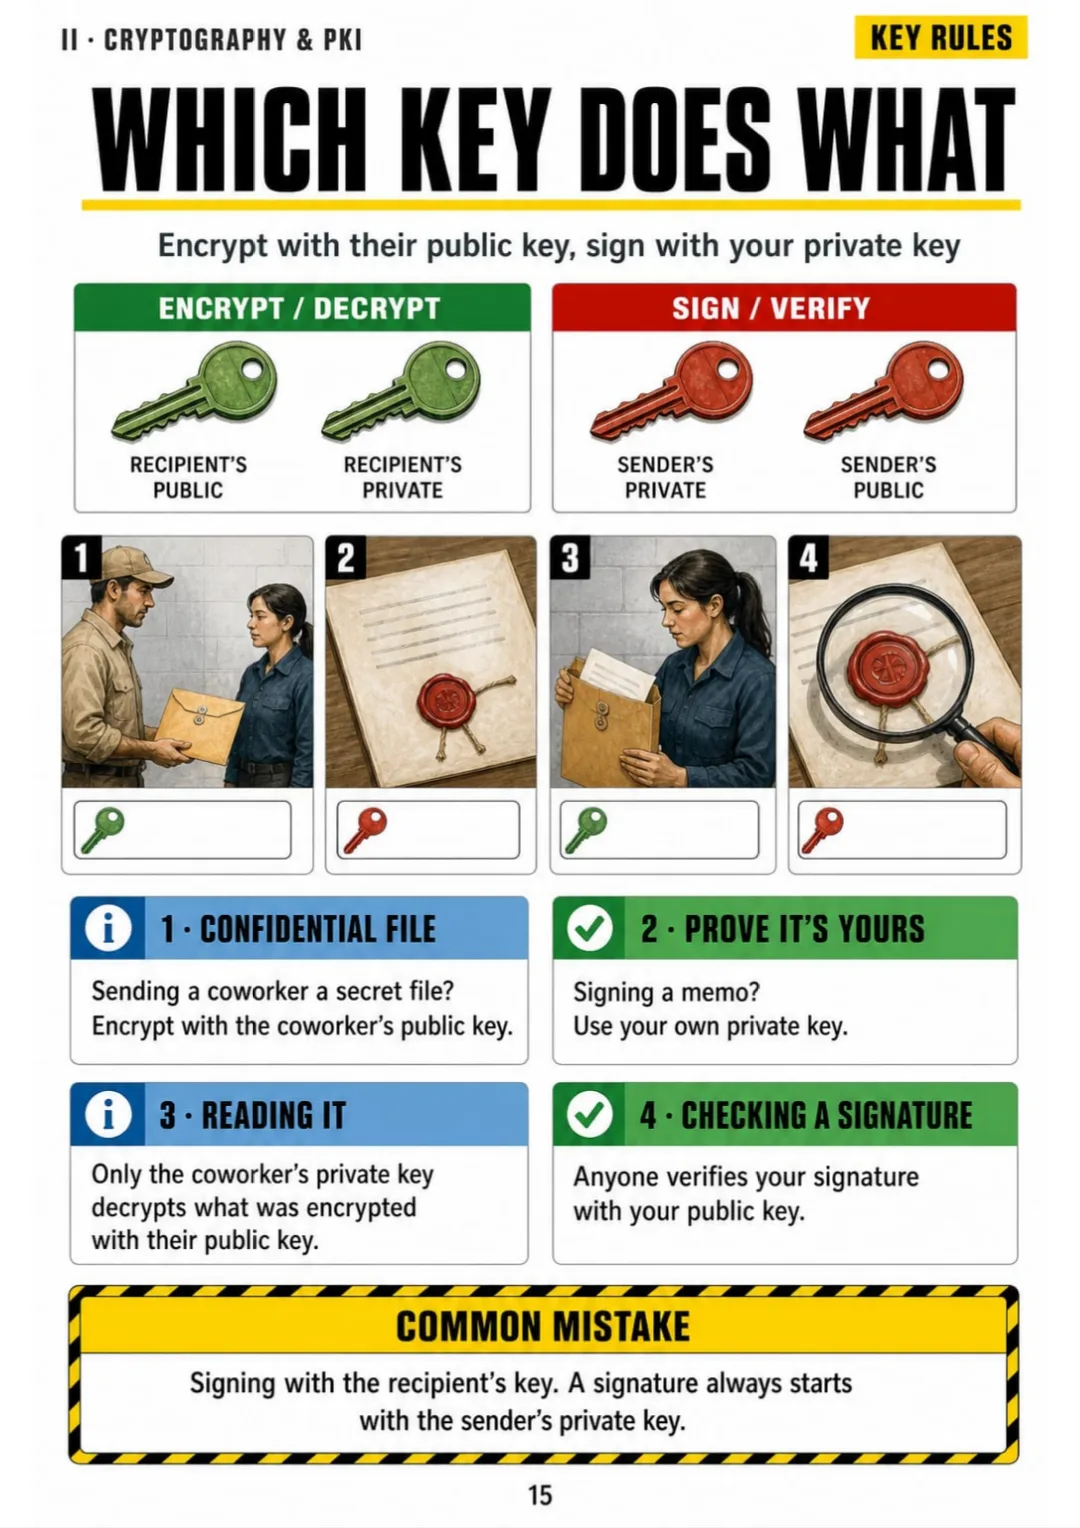
Confidentiality: recipient's public key · Signature: sender's private key
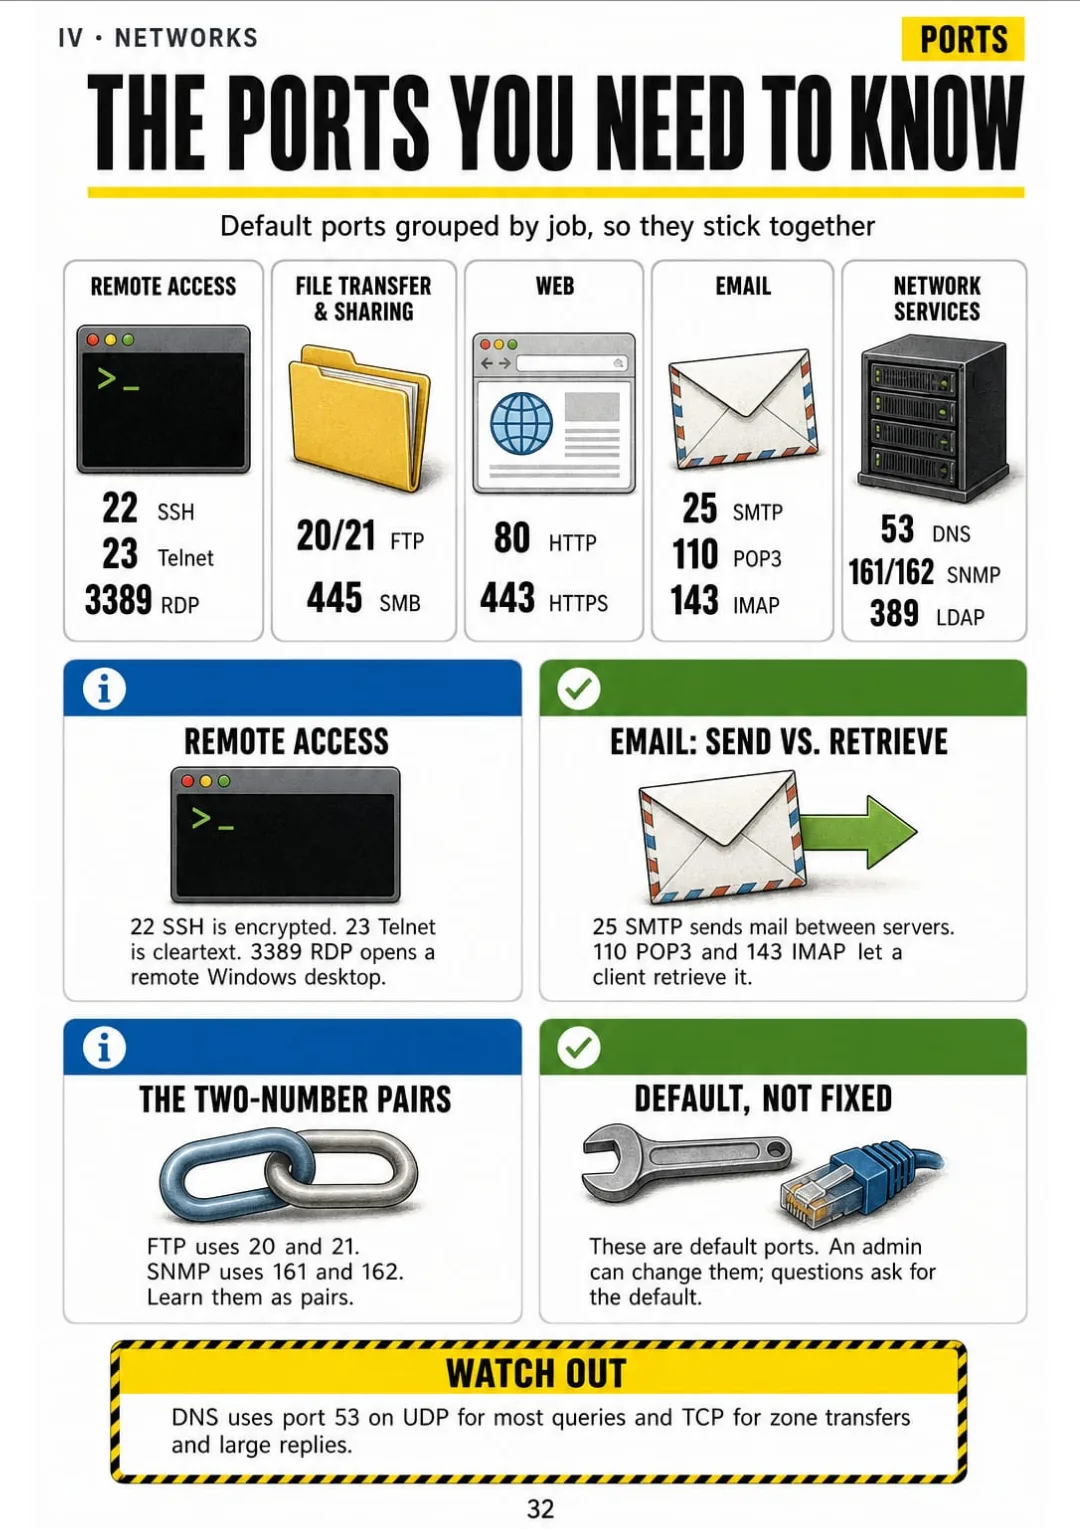
22 SSH, 23 Telnet, 53 DNS, 443 HTTPS, 3389 RDP: grouped by what they do
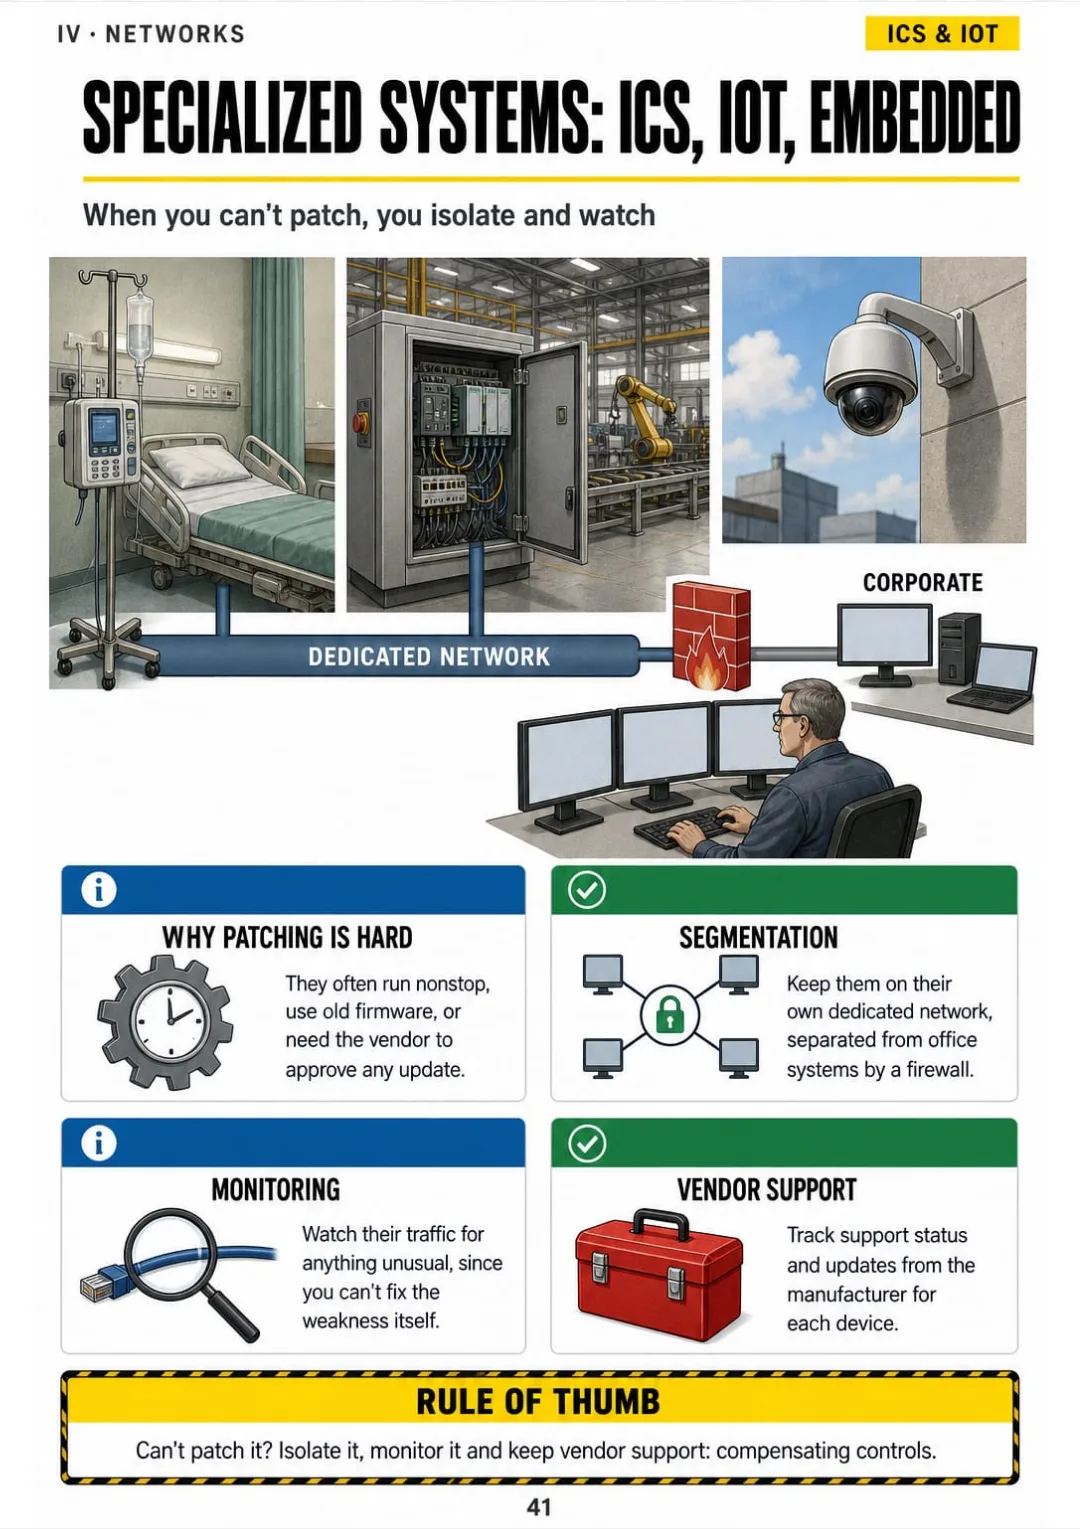
ICS/SCADA, IoT, embedded: segmentation, dedicated network, monitoring, vendor support
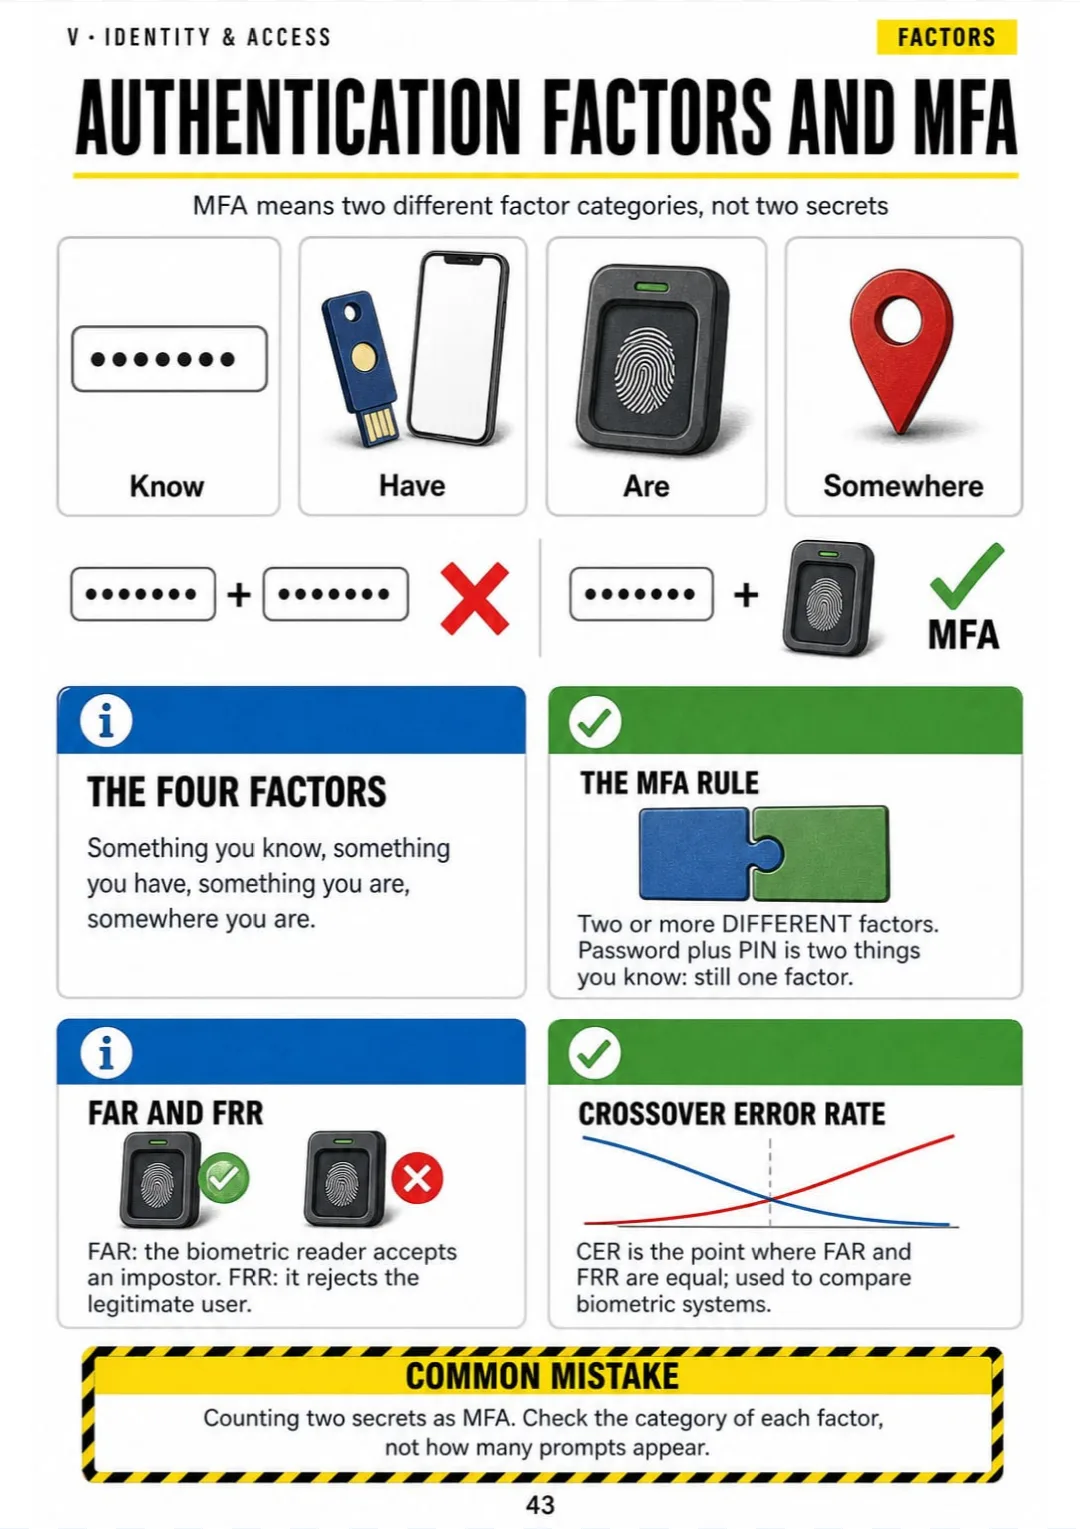
4 factors, 1 rule: MFA needs two different categories
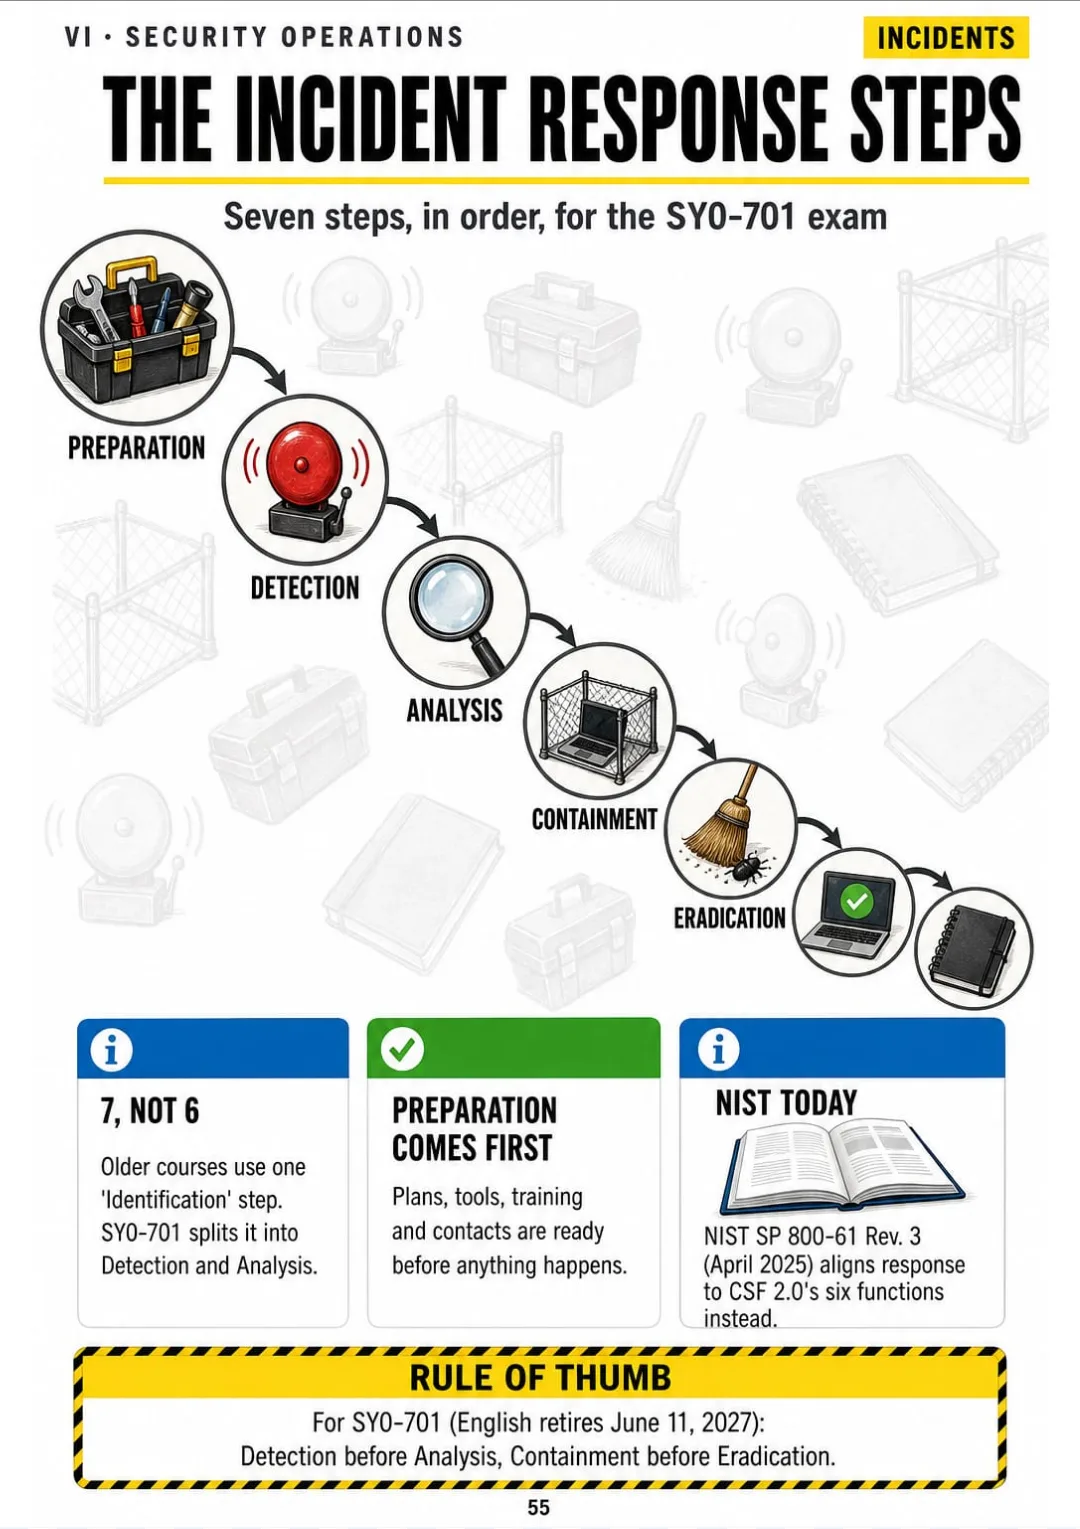
Preparation → Detection → Analysis → Containment → Eradication → Recovery → Lessons learned.
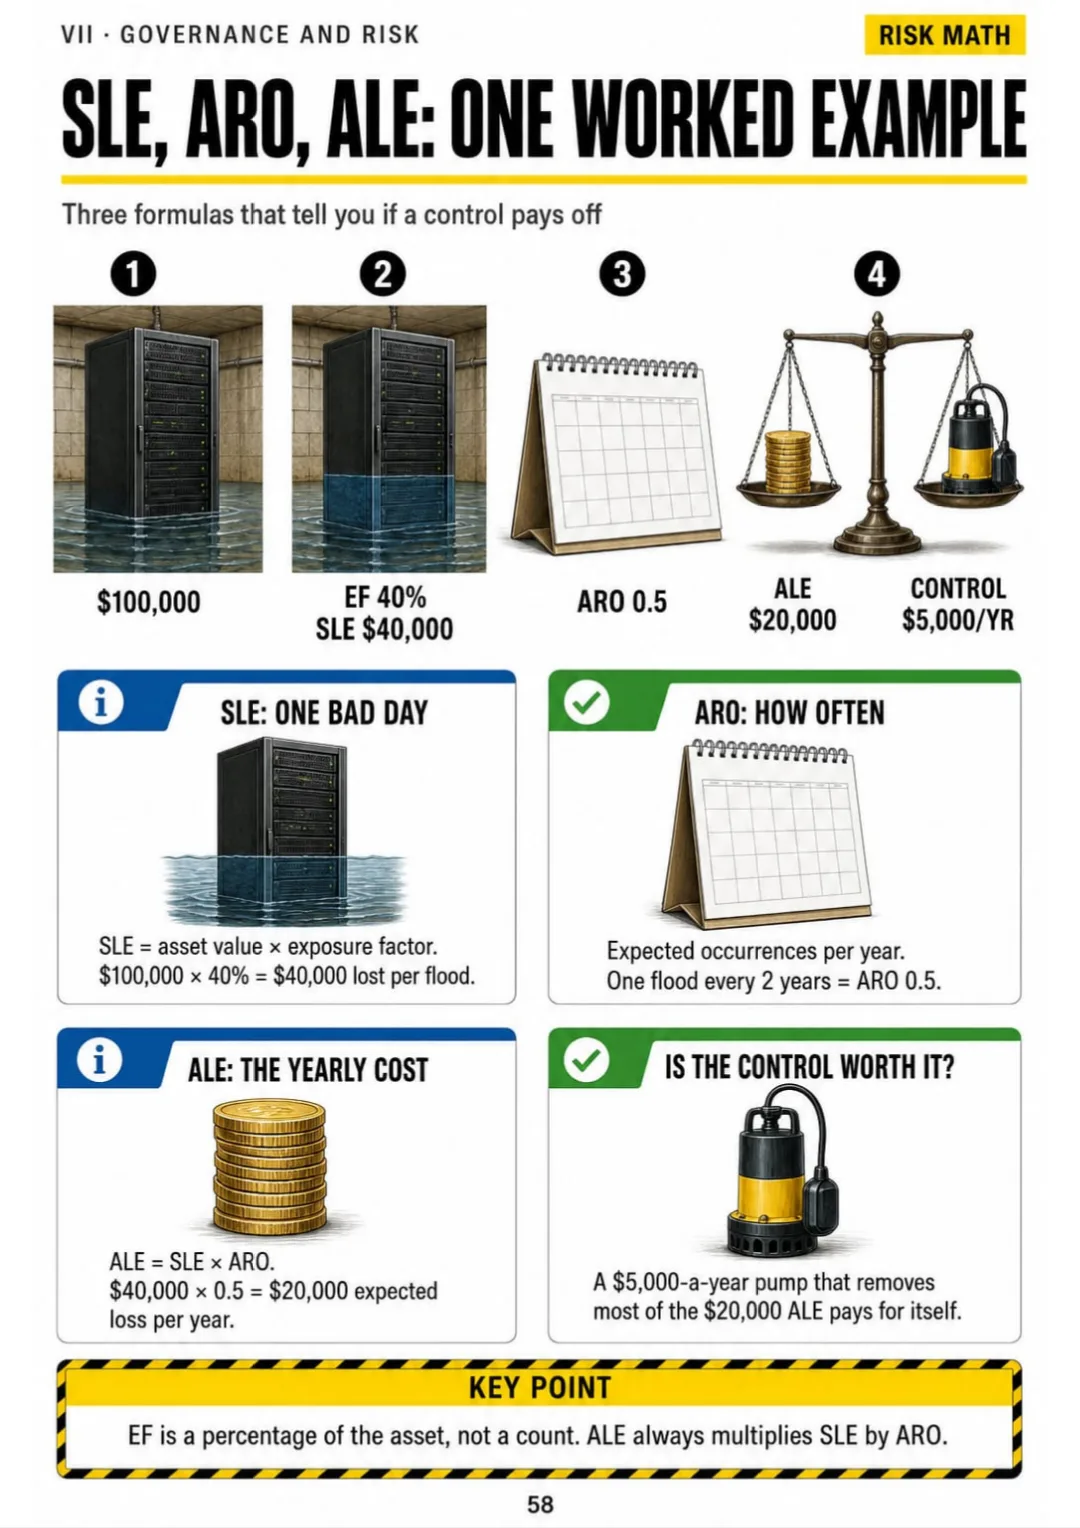
SLE = asset value × EF · ALE = SLE × ARO, worked out with a flooded server
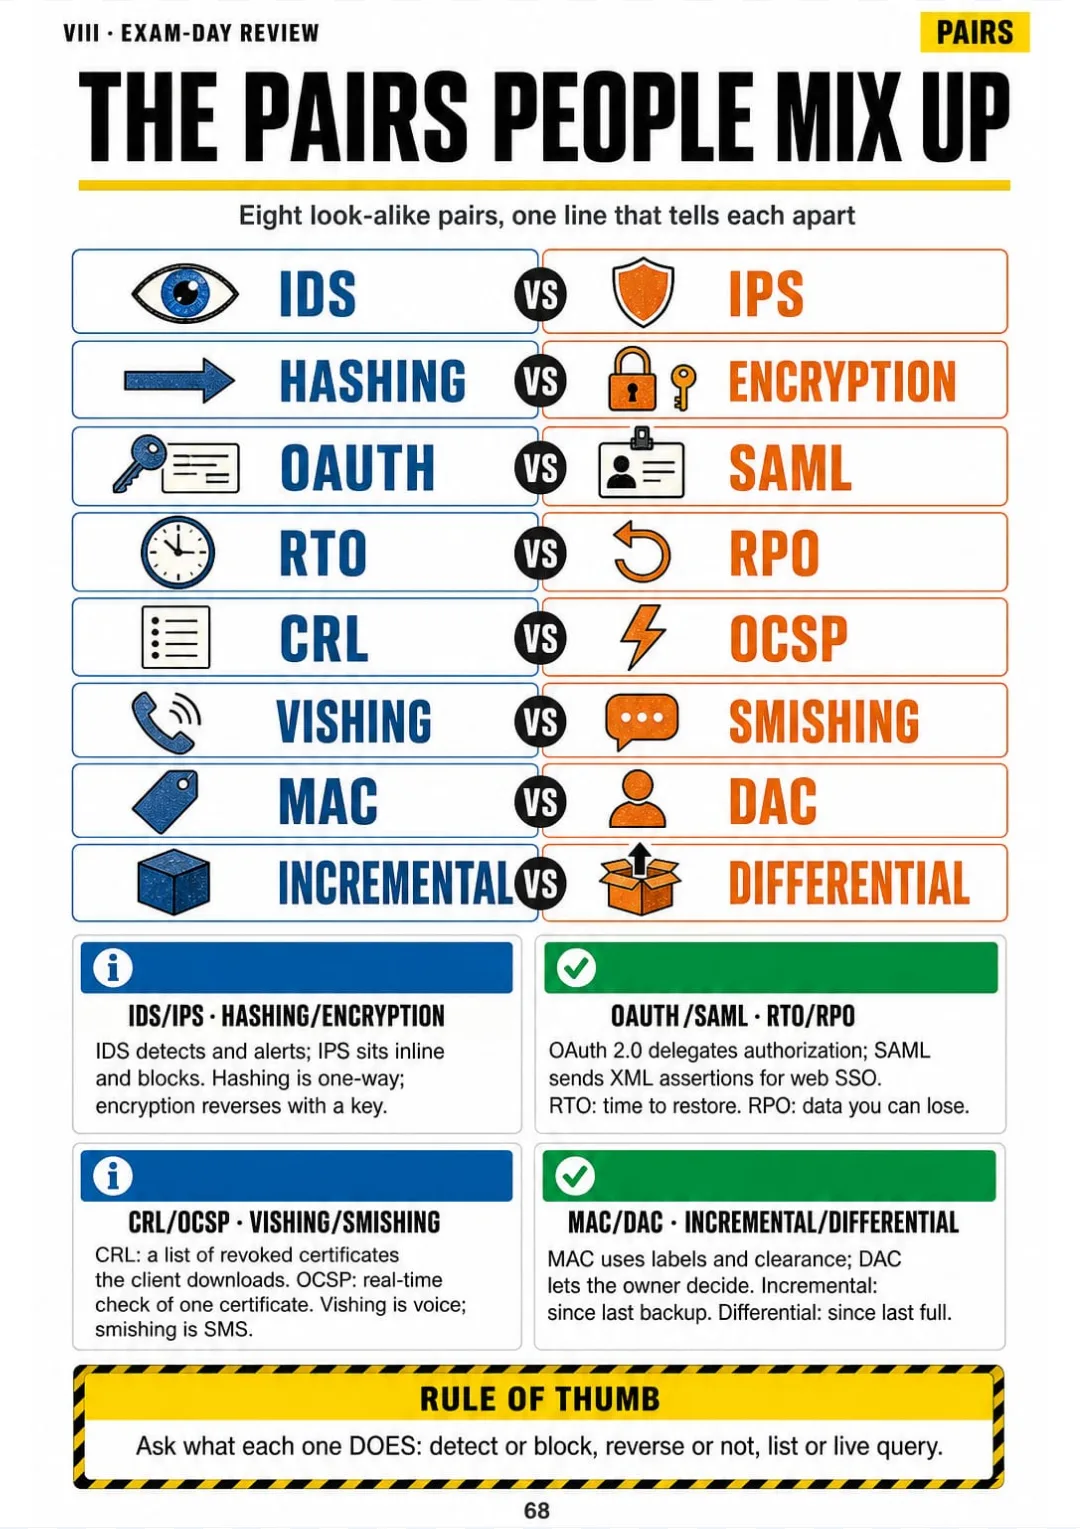
IDS detects, IPS blocks · RTO is time, RPO is data · CRL is a list, OCSP is live

Take a Look at the 8 Parts and 65 Topics

Security Basics

pp. 5-13
  1. How to Read Every Page: Threat → Control → First Move
  2. The CIA Triad
  3. AAA and Non-Repudiation
  4. Control Categories: Technical, Managerial, Operational, Physical
  5. Control Types: Preventive to Compensating
  6. Zero Trust: Never Trust, Always Verify
  7. Physical Security and Sensors
  8. Deception: Honeypot, Honeynet, Honeyfile, Honeytoken
  9. Change Management Without Surprises

Cryptography and PKI

pp. 14-21
  1. Symmetric vs. Asymmetric Encryption
  2. Which Key Does What
  3. Hashing, Salting and Key Stretching
  4. Digital Signatures Step by Step
  5. The Certificate Chain of Trust
  6. Revocation: CRL vs. OCSP
  7. Protecting Data in Every State
  8. Where Keys Live: HSM, TPM, Escrow, Key Exchange

Threats, Attacks and Vulnerabilities

pp. 22-31
  1. Threat Actors and What Drives Them
  2. Social Engineering Vectors
  3. Malware Types Side by Side
  4. Password Attacks and Their Fingerprints
  5. Network Attacks
  6. Application Attacks
  7. Cryptographic Attacks
  8. Vulnerability Types
  9. Indicators of Compromise
  10. Mitigation Techniques

Networks and Security Architecture

pp. 32-42
  1. The Ports You Need to Know
  2. Insecure Protocol → Secure Replacement
  3. Subnetting, One Worked Example
  4. Network Zones: Screened Subnet, Jump Server, Proxy
  5. Firewalls and Rule Order
  6. IDS vs. IPS
  7. VPNs and Secure Tunnels
  8. Wireless Security
  9. Cloud Models and Shared Responsibility
  10. Specialized Systems: ICS/SCADA, IoT, Embedded
  11. Resilience: RTO, RPO and Backups

Identity and Access

pp. 43-48
  1. Authentication Factors and MFA
  2. Access Control Models
  3. Least Privilege, Separation of Duties, PAM
  4. SSO and Federation: SAML, OAuth, OpenID Connect
  5. The Account Lifecycle
  6. Passwords and Passwordless

Security Operations

pp. 49-57
  1. Secure Baselines and Hardening
  2. Endpoints and Mobile Devices
  3. Vulnerability Management Cycle
  4. Assets and Data Sanitization
  5. Logs, SIEM and Automation
  6. Email Security: SPF, DKIM, DMARC
  7. The Incident Response Steps
  8. Containment: What You Do First
  9. Digital Forensics: Order of Volatility

Governance, Risk and Compliance

pp. 58-64
  1. Quantitative Risk: SLE, ARO, ALE
  2. Risk Responses and the Risk Register
  3. Policies, Standards, Procedures, Guidelines
  4. Third-Party Agreements
  5. Data Roles and Classification
  6. Audits and Penetration Tests
  7. Security Awareness That Works

Exam-Day Review

pp. 65-69
  1. The 5 Domains on One Page
  2. Reading a Scenario Question
  3. Performance-Based Questions
  4. The Pairs People Mix Up Most Often
  5. Final-Week Checklist

Who This Book Is For

You're starting Security+

Each topic on one page, always in the same layout: the drawing first, then the box with what to remember. What you studied Tuesday is one page away on Thursday.

Your exam date is close

The last part puts the 5 domains on one page, the pairs people mix up and a final-week checklist. You review by page, not by chapter.

You already work in IT

Help desk, sysadmin or a defense contract that now asks for the cert: you see phishing and lockouts every week. The book puts the exam's names on what you already do.

Plus: 2 Free Books

Exam-Style Practice Questions with Explained Answers
BONUS 1

Exam-Style Practice Questions with Explained Answers

Practice the way the exam asks: multiple-choice and scenario questions, each answer explained in one line so you see why the other options are wrong.
Acronyms, Ports & Common Mistakes Review Sheets
BONUS 2

Acronyms, Ports & Common Mistakes Review Sheets

The acronyms, the port numbers and the mistakes that mix people up most often, on a few printable pages you can review the night before.

30-Day Guarantee

30-day guarantee: if a file doesn't open, if the content isn't what the product page describes, if you were charged twice or the email never arrived, write to us and we'll refund you in full. You pay once. No subscriptions.

Frequently Asked Questions

Is it for me if I work full-time and study for Security+ at night?

Yes. Each topic fits on one page, so one evening covers a few pages. The drawings aren't dumbed down: they carry the exam's real content, like the ports by group, which key does what, SLE × ARO and the 7 incident response steps. Each term is explained the first time it appears, but it doesn't teach IT from zero: if you've never worked with networks, pair it with a basic networking course.

Where does the content come from?

It's checked against the Security+ exam objectives currently in force, plus NIST SP 800-207 for zero trust. The seven incident response steps follow the exam's own model. The exam is changing versions: if you're booked on a newer one, compare the table of contents on this page with its objectives before you buy.

Is this official material?

No. It's an independent study book, not affiliated with or endorsed by CompTIA. It doesn't include an exam voucher or a certificate: you book and pay for the exam separately.

Does it replace a course or training?

No. It's what you use alongside your course: the videos explain, and here each topic is on one page you can look at again the night before. Use it with your labs and your own practice.

Are the practice questions the ones on the exam?

No. Every question is written for this book, in the style of the exam. None of them are real exam questions.

When and how do I get it?

As a PDF by email: the book and the 2 bonus books go to the address you enter at checkout.

Do I have to pay every month?

No. It's a one-time payment.

Can I have it on paper?

Yes. The PDF is printable, at home or at a print shop.

How does the refund work?

You have 30 days. We refund everything if the file won't open, if the book isn't what you see on this page, if you were charged twice or if the email doesn't arrive: just email us.

US$ 27US$ 63
Get the book · US$ 27

This is a digital PDF book sent to your email: nothing is printed or shipped.

More books on this topic

Networking & Cabling Illustrated

Networking and structured cabling explained one topic per page, each with a big, clear drawing: RJ45 pinouts T568A and…

From US$ 27 US$ 63

Video Security Systems Illustrated

Video surveillance explained one topic per page, every concept drawn: system architecture, camera types, lenses and…

From US$ 27 US$ 63

Locksmith Illustrated

An illustrated locksmith book for license and certification prep: pin tumbler cylinders, key blanks and bitting…

From US$ 27 US$ 63

Fiber Optic Technician Illustrated

Fiber optics explained one topic per page, every concept drawn: singlemode vs. multimode, LC/SC/MPO and UPC vs. APC…

From US$ 27 US$ 63

Cabling Installer Illustrated

Structured cabling explained one topic per page, every concept drawn: the 6 subsystems as one path, Cat 5e vs Cat 6 vs…

From US$ 27 US$ 63

Tower Technician Illustrated

Get ready for the TTT-1 written exam with a book you can actually picture: tower anatomy, fall protection, 100%…

From US$ 27 US$ 63